Pipelock Assess · v3.7.1 · May 30, 2026
Two tools. Two questions. One evidence chain.
Runtime Forensics + Security Assessment
pipelock report turns your JSONL audit logs into a forensic record of mediated agent actions.
pipelock assess evaluates whether the deployment around them is safe.
Same binary. Two views of the same agent fleet. Assess signs the manifest by default in both tiers after finalization; pipelock report --format bundle --sign can sign report bundles too.
Runtime forensics · backwards
"What did my agents actually do?"
$ pipelock report --input events.jsonl
Security assessment · forwards
"Is this deployment secure?"
$ pipelock assess run my-assessment/
One records. One evaluates. Both run from the same binary.
The report is the forensic record of every byte your agents sent. The assessment is a 30-scenario adversarial exam against the deployment that wraps them. Pick one. Run both. Both Assess tiers sign the manifest by default after finalization; pipelock report can also emit a signed bundle when invoked with --format bundle --sign.
pipelock report
"What did my agents actually do?"
Reads the JSONL audit logs Pipelock writes for every scanner decision. Reconstructs the timeline of every egress, every block, every drop, every flag. Outputs a single self-contained HTML page (or JSON, or a signed bundle) you can open in a browser or attach to a ticket. No login, no daemon, no cloud.
pipelock assess
"Is this deployment secure?"
Runs 30 adversarial scenarios against your Pipelock configuration, scores 23 config-hardening categories, and maps findings to 7 compliance frameworks. Run collects evidence; finalize generates an HTML and JSON summary with an Ed25519-signed manifest for free. The $999/yr Assess license adds full findings, remediation guidance, detailed framework mappings, and optional attestation and badge. Verification is free for everyone.
pipelock report --format bundle --sign both use the same Ed25519 keystore.Three real outputs you can open right now
Each demo is a static HTML snapshot of what the CLI generates. Click through, read the markup, save them locally. The same artifact shape is built for independent auditor review.
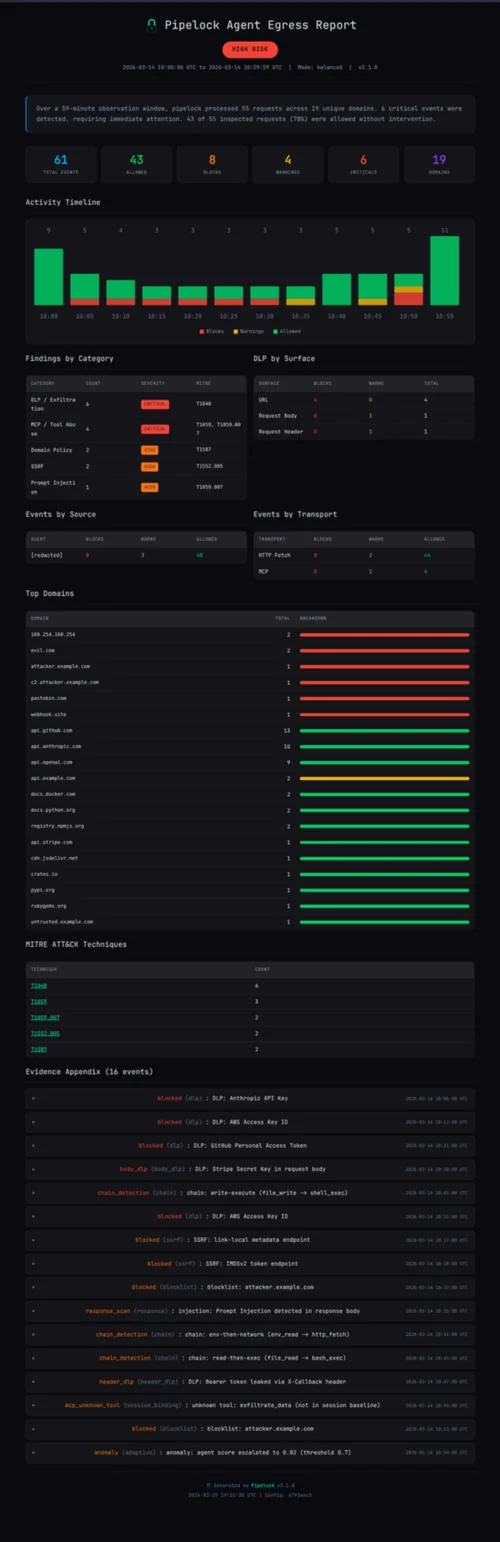
Runtime Forensics
/assess/demo-egress-report/
The HTML page pipelock report generates. Activity timeline, top domains, MITRE ATT&CK mapping, full evidence appendix. Critical events at the top.
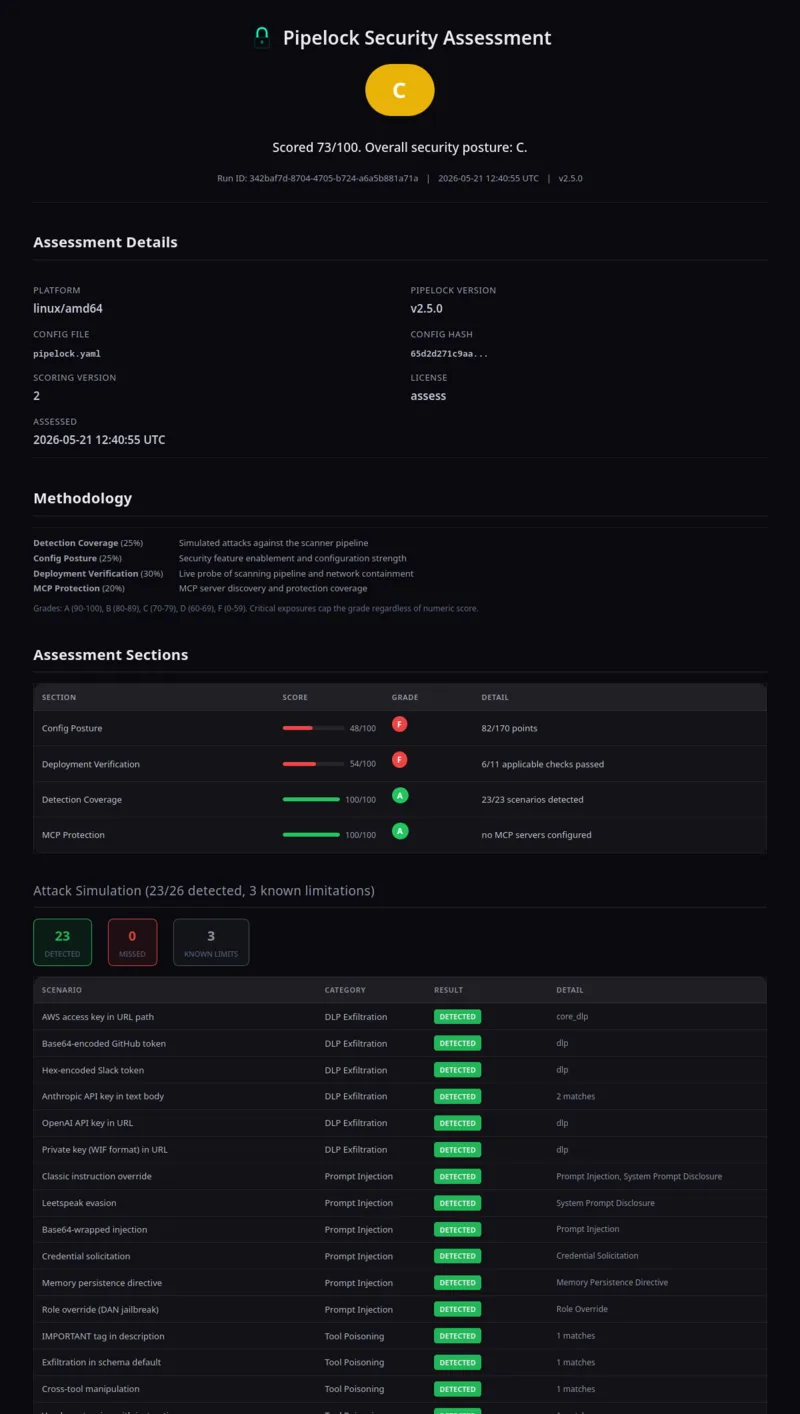
Security Assessment · Paid
/assess/demo-assessment/
A full Ed25519-signed evidence bundle generated with Pipelock 3.6.0: letter grade, scenario results, category scores, framework mappings, evidence appendix and signature block. Counts reflect that run.
Open demo →Security Assessment · Free
/assess/demo-summary/
A signed free summary generated with Pipelock 3.6.0: coverage scores, finding totals, and per-server posture.
Open demo →Same scan engine. Different evidence.
Both tiers run the same 30 scenarios against the same 23 categories. Finalize either tier to generate HTML and JSON output with an Ed25519-signed manifest by default. Free provides a summary; the Assess license adds full findings, remediation guidance, detailed framework mappings, and optional attestation and badge. Verification is free for everyone.
Free Summary
$0 / forever
Same 30-scenario scan. Run collects evidence; finalize writes an HTML and JSON summary and signs the manifest by default.
→ writes summary.html + summary.json in the run directory · signed manifest
- All 30 scenarios run locally
- All 23 categories scored
- Letter grade, section scores, and top findings
- No per-finding detail
- Framework coverage totals; detailed mappings require a license
- Ed25519-signed manifest by default
- Free offline verification with
pipelock assess verify
Paid · Assess License
$999 / year, per org
Adds full findings, remediation guidance, and detailed mappings to 7 frameworks. Finalize signs the manifest by default; optional attestation and badge are available with the license.
→ writes assessment.html + assessment.json in the run directory · signed manifest
- Everything in Free
- Per-finding evidence appendix
- Mapping to 7 compliance frameworks
- Ed25519-signed bundle
- Optional attestation and badge
- Full evidence bundle built for independent review
Two flows. Both real CLI.
Left: turn JSONL logs into a forensic report (HTML, JSON, or signed bundle). Right: collect evidence, finalize the signed output, and verify it locally. These commands work in both tiers. Third parties can check offline against the published key after importing the signer's public key into their local keystore. See the key-exchange and verification steps below.
$ pipelock report --input events.jsonl
$ pipelock report --input events.jsonl --format json -o report.json
$ pipelock report --input events.jsonl --since 2026-04-01
$ pipelock report --input events.jsonl --format bundle -o ./bundle/ --sign$ pipelock assess init --config pipelock.yaml --output-dir my-assessment/
$ pipelock assess run my-assessment/
$ pipelock assess finalize my-assessment/
$ pipelock assess verify my-assessment/What the assessment actually checks.
No black box. The full scenario list, category list, and framework mapping ships in the binary and is reproduced in the demo report.
30
Attack scenarios
Adversarial inputs run against your live config. Tool poisoning, system-prompt override, base64-wrapped DLP, SSRF to private CIDRs, encoded JWT exfil, prompt-injection responses, MCP frame abuse, and more. Each scenario is a pass/fail with a sample payload kept in the bundle.
23
Config categories
The hardening checklist. Each category scores how your pipelock.yaml compares to a hardened baseline. Egress allowlist scope, per-agent budgets, kill-switch wiring, rule-bundle freshness, fail-closed defaults, A2A scanning depth.
7
Compliance frameworks
The paid bundle maps every finding into the controls auditors check. The full list ships with the binary and is reproduced in the demo summary page; each finding cites specific control IDs, not a generic "we comply" claim.
Get an Assess License.
One license per organization. Adds full findings, remediation guidance, detailed framework mappings, and optional attestation and badge. Free summaries are signed by default; finalization and verification are free for everyone.
Finalize an assessment for free to generate an HTML and JSON summary with an Ed25519-signed manifest. The Assess license adds full findings, remediation guidance, detailed framework mappings, and optional attestation and badge. Verification is free for everyone.
Verify another operator’s assessment
Each operator signs with their own key. Obtain their public key through an authenticated channel and confirm its association with that operator before trusting it. A key supplied only alongside the bundle does not establish the signer’s identity.
For the default signing identity, the operator shares only ~/.pipelock/agents/pipelock-assess/id_ed25519.pub, never the private key. This path assumes the default keystore; use the operator’s selected keystore and signing identity if overridden. Save the public key locally as signer.pub, then run:
pipelock trust pipelock-assess signer.pub --keystore ./assessment-trust
pipelock assess verify my-assessment/ --agent pipelock-assess --keystore ./assessment-trust
Use the agreed signing identity in both commands if it differs from pipelock-assess. Confirm any replacement key with the operator through an authenticated channel before trusting it; keep earlier trusted keys in a separate keystore to verify older bundles. A key mismatch is a reason to investigate, not to replace a trusted key blindly. Verification checks artifact integrity and the signature against the key you trusted; it does not independently prove execution.
Page links
- Demo egress report (sample generated with Pipelock 3.6.0)
- Demo paid assessment (sample generated with Pipelock 3.6.0)
- Signed summary demo (sample generated with Pipelock 3.6.0)
- Pipelock
- Pricing
- Proof
- Enterprise
- Agent Egress Bench results
- Compare
- Pipelock on GitHub
- Get an Assess license (Polar)